- Our registered Charity no. 1164762
AI, Data and Compliance: Q&A with an Expert
The Opportunities and Threats of AI: Q&A with an Expert
7 October 2026
As AI tools become part of everyday work, so does the need for effective compliance.
Getting it right shouldn’t be stressful or time-consuming. With the right approach, it can be straightforward and reassuringly simple.
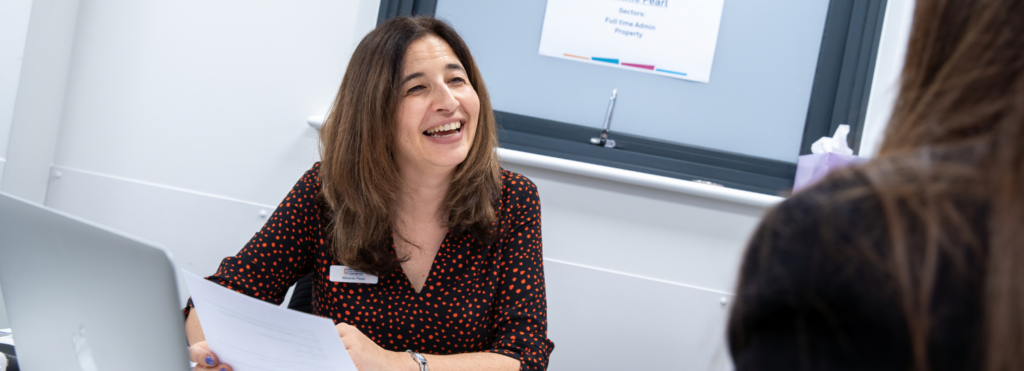
Rivka Abecasis is an independent specialist in AI and data governance, compliance and operations. She helps businesses, charities and freelancers put the right policies, processes and safeguards in place, in plain English that people can actually use.
Here Rivka answers frequently asked questions about using AI responsibly, protecting the personal information of the people you work with, and making compliance less daunting. Her answers apply whether you run a business, a charity or work for yourself.
Q: What are the first things to consider about using AI?
A: I encourage people to start with three simple questions.
First, do you know which AI tools your team is using? You might assume nobody is using AI, only to discover that someone has a personal AI account and is pasting entire client emails into it to help draft replies.
Second, do you know what those tools are doing with your data? Could the information you put in be used to train the AI? Have you shared a link or document in a way that exposes information to other people? These are questions worth asking before you put personal information into any tool.
Third, are your settings right, and are you using the right version of the tool for your needs? Different tools, accounts and settings offer different protections. You need to understand what you’re using and whether it’s appropriate for your work.
Once you know the answers, agree with your team what can and cannot go into AI tools, and write it down. If you work for yourself, the same questions apply to your own use.
Q: What policies should you have in place?
A: An AI policy is one of the first things I’d recommend. It should explain how people in your organisation can use AI, what information they can put into it and what they must avoid.
It also needs to work alongside your existing data protection arrangements. Some organisations are updating their privacy notices to explain how they use AI, particularly where personal information is involved.
Think about the information you handle. An employer holds salaries and employment histories. A doctor’s surgery handles clinical notes. A charity may support people through difficult personal circumstances. That information isn’t all the same. Some of it, such as health details or religious beliefs, is classed as special category data under data protection law and needs extra care.
There isn’t one policy that suits every organisation. It needs to reflect what you actually do, the information you hold and the tools you use.
The key is to make it practical. As I often say, a policy that no one understands protects no one. There’s little point writing a 30-page document that sits in a shared drive and is never opened.
Q: Is having a good policy in place enough?
A: No. Your team also needs to understand it and know how to put it into practice. That’s why my policies come with a plain-English guide, so people can use them day to day.
The Information Commission’s Office (ICO) expects organisations to train their staff on data protection. If your team uses AI with personal information, that training needs to cover it. I help clients create short training videos, questionnaires and team discussions, so training never feels intimidating. That’s what governance means in practice: not rules on paper, but people who know them and use them.
It helps to see the risk in terms of your own work. Imagine a bookkeeper pasting a client’s bank statements into a free AI tool to sort the transactions. Would you be comfortable with that going into a tool without knowing where it ends up? Would your client?
When you frame it as looking after the people you serve, it makes sense to everyone. Nobody wants to risk the trust they’ve built with their clients and the people they support.
Q: What happens if something goes wrong?
A: Having a policy, training your team and being able to show you’ve taken it seriously all form part of a responsible approach. Even so, a policy isn’t a guarantee against a fine or other consequences.
What matters most is that the right person knows what to do. Who in your organisation needs to be told, and how quickly? If you work alone, who would you turn to? When does it need to be reported outside your organisation?
Some data breaches must be reported to the ICO without undue delay and, where possible, within 72 hours of you becoming aware of them. In some cases the people affected must be told too. That isn’t the moment to be working out the process for the first time. Have a simple procedure in place, and make sure the people who need it know where it is.
Q: Can you simply ask a chatbot to write an AI policy?
A: You can, and many people do. Would I advise it? Not on its own. A chatbot can only work with what you give it.
A good policy draws on knowing which laws apply to you, how they interact, and how the policy fits with the rest of your organisation, from your privacy notice to your other policies. Without that, you can end up with something that sounds convincing but doesn’t fit how you actually work. AI tools can also be out of date or miss important details.
If you work for yourself, you might research the relevant guidance, draft your own policy and ask someone else to review it. You can’t mark your own work. Sometimes a DIY approach is perfectly reasonable; sometimes it’s worth bringing in a specialist. It depends on your organisation, the information involved and the level of risk.
My approach is about guidance and empowerment. I want people to understand why something is needed and where the requirement comes from. Whoever gives you guidance, ask what it’s based on and where you can check it. That way, when your organisation changes or the rules do, you know what to revisit.
Q: Where can you get further help?
A: You don’t have to do it all yourself, and you don’t need a full-time compliance officer to get this right.
Some organisations come to me to get set up: the right policies in place and a team that knows how to use them. Others need help with a single policy, a review of their processes or a second opinion on their current approach. Some then keep me on as their fractional specialist, so their policies stay up to date as the rules change.
Work Avenue is also a great starting point. Its workshops, advice and wider network support charities, start-ups and business owners, including finding specialist help where it’s needed.
My message is simple: don’t panic, but don’t ignore it either. Start by understanding what information you hold, which tools you and your team are using, and what safeguards you have in place.
As I often say, you don’t know what you don’t know. I learned that early, when I lost my first business for want of one document. You don’t have to know everything. You just need to know enough to ask the right questions, and the right person.
Whether you’re just starting out or catching up, I’m always happy to talk. Visit www.rivkaabecasis.com or email [email protected].